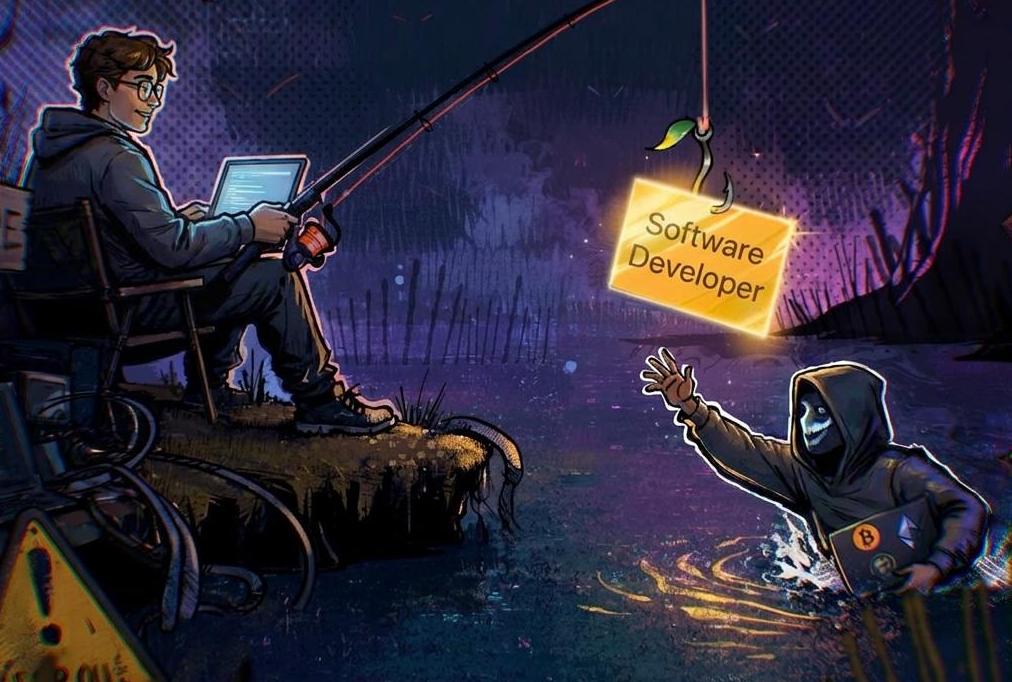

Consensys Unknowingly Outsourced Developer Work to North Korean Operative
In a startling revelation that underscores the growing sophistication of state-sponsored cyber threats, Consensys—the powerhouse behind the MetaMask wallet and a cornerstone of the Ethereum ecosystem—has disclosed that it unknowingly engaged a developer tied to North Korea. The incident highlights a dangerous new trend in the tech industry: the use of "sleeper" developers who infiltrate legitimate companies through reputable intermediaries to gain internal access and facilitate financial theft.
The breach did not occur through a traditional software vulnerability or a phishing attack, but rather through a calculated social engineering scheme designed to bypass standard corporate vetting processes. By leveraging a third-party service provider, the operative managed to embed themselves within the Consensys workforce, posing as a skilled remote engineer.
The Anatomy of the Infiltration
According to reports, the individual was introduced to Consensys via a "reputable third-party service provider." This is a critical detail, as it suggests that the North Korean operative did not simply apply via a job board with a fake resume, but instead utilized a layer of institutional trust. By partnering with a recruitment or outsourcing firm that Consensys already trusted, the operative was able to circumvent the rigorous background checks typically associated with high-security blockchain development.
Once inside, the developer functioned as a standard contractor, contributing to the codebase and integrating into the team's workflow. This "long-game" approach is a hallmark of the Lazarus Group and other North Korean state-sponsored entities, which have pivoted from brute-force hacking to sophisticated identity theft and professional infiltration. By gaining a foothold inside a company, these actors can identify vulnerabilities in the internal infrastructure, steal private keys, or plant "backdoors" in the code that can be exploited months or years later.
The Investigation and Discovery
The deception was only uncovered after a rigorous internal investigation. While Consensys has not released the full forensic details of the discovery, it is evident that a combination of behavioral analysis and digital forensics flagged the developer's activities as suspicious. In the world of cryptocurrency, where "code is law," the discovery of a rogue actor within the development pipeline is a nightmare scenario, as it threatens the integrity of the software used by millions of users.
The discovery comes at a time when the U.S. Department of Justice and the FBI have repeatedly warned that North Korea is aggressively targeting the Web3 and DeFi sectors to fund its weapons programs. The shift from external attacks to internal infiltration represents a significant escalation in the threat model for blockchain firms.
The Broader Threat: The "Fake Developer" Trend
The Consensys incident is not an isolated event. Over the past 24 months, the cybersecurity community has observed a surge in North Korean operatives creating elaborate fake personas on LinkedIn and GitHub. They build impressive portfolios, contribute to open-source projects, and network with industry leaders to create a veneer of legitimacy.
Once they secure a remote position, these developers often perform their duties diligently to avoid suspicion, while simultaneously searching for "crown jewels"—such as administrative credentials, seed phrases, or undocumented API keys. This method of infiltration is particularly effective in the remote-first culture of the crypto industry, where developers are often hired based on their technical proficiency and GitHub history rather than face-to-face interviews and rigorous identity verification.
How the Industry Can Combat Infiltration
The Consensys breach serves as a wake-up call for the entire Web3 ecosystem. To prevent similar occurrences, companies must move beyond traditional hiring practices and adopt a "Zero Trust" approach to personnel management. Key strategies include:
1. Enhanced Due Diligence for Third-Party Vendors: Companies can no longer assume that a reputable outsourcing firm has performed adequate KYC (Know Your Customer) checks. Blockchain firms must demand transparent verification processes from their partners.
2. Implementation of Least Privilege Access: Developers should only have access to the specific modules of code they are working on. Broad access to the core architecture should be restricted and require multi-signature approval.
3. Rigorous Code Reviews: All contributions, regardless of the developer's seniority or tenure, must undergo strict peer reviews to ensure no malicious code or "logic bombs" are being inserted into the production environment.
4. Behavioral Monitoring: Utilizing AI-driven security tools to monitor for unusual access patterns, such as a developer accessing sensitive directories outside of their assigned tasks or logging in from unexpected geographic locations via VPNs.
Final Thoughts
Consensys' transparency in reporting this incident is a commendable step toward industry-wide security. However, the fact that a state-sponsored actor could penetrate one of the most prominent firms in the Ethereum space proves that the battle for security is no longer just about patching bugs—it is about verifying the humans behind the code.
As the line between legitimate remote work and state-sponsored espionage blurs, the crypto industry must prioritize human intelligence and identity verification as much as it prioritizes cryptographic security. Failure to do so could leave the door wide open for adversaries who are patient, disciplined, and increasingly skilled at blending in.